Binance Investigation Reveals a Months-Long Cyberattack
Binance has outlined how attackers compromised employee computers and obtained internal credentials before stealing approximately $6.3 billion in digital assets from its wallet infrastructure. The exchange’s investigation describes a campaign that began months before the October 29 breach, combining malicious software, social engineering and access to internal systems.
The attackers did not rely on a single entry point. Instead, they reportedly gathered information about Binance’s wallet team, targeted software engineers and used compromised devices to reach systems involved in authorizing cryptocurrency transactions. The exchange published its findings in a postmortem shared on X on Tuesday.
The incident highlights how cyberattacks against cryptocurrency platforms can extend beyond direct attacks on blockchain infrastructure. In this case, the reported intrusion began with employees and their work devices before reaching the systems responsible for wallet operations.
Malicious Software First Appeared During an AI Tool Setup
Binance’s account traces the campaign back to June, when an engineer downloaded a tampered software package while configuring an AI coding tool. The exchange detected the malware and replaced the affected device. However, the attackers had already collected information about the team responsible for wallet operations.
A second intrusion attempt reportedly took place in September. Attackers impersonated recruiters and approached another software engineer with what appeared to be a coding assignment for a job opportunity. The employee downloaded a malicious file disguised as part of the recruitment process, allowing the attackers to compromise the engineer’s work computer and evade the exchange’s security protections.
The recruitment approach gave the attackers another route into Binance’s environment. Rather than attempting to breach the exchange’s systems directly, they used a seemingly routine professional interaction to target an employee with access to internal resources.
Stolen Credentials Opened Access to Wallet Infrastructure
The next reported stage occurred on October 20. Attackers used the compromised computer and an internal AI tool to access the systems of two additional engineers. They obtained deployment credentials, which later allowed malicious software to be installed within Binance’s wallet infrastructure on October 29.
The attackers then reached the exchange’s internal wallet-signing service. This service authorizes cryptocurrency transactions, making access to it particularly sensitive. By compromising the signing process, the attackers could move funds outside Binance’s normal withdrawal procedures.
Binance co-CEO Richard Teng described the incident as a prolonged operation rather than an isolated security failure. “This wasn’t one mistake or one breach — it was a months-long campaign,” Teng said in a post on X.
The sequence described by Binance shows how access to employee devices, internal credentials and deployment systems can create a path toward critical financial infrastructure. It also demonstrates why recruitment-related files and third-party software packages can become security risks when they are not adequately verified.
EIP-7702 and MPC Complicated the Response
Binance said the attackers also exploited Ethereum’s EIP-7702 mechanism during the incident. The proposal allows externally owned accounts, commonly used as standard crypto wallets, to delegate certain transaction capabilities to smart contracts. This can enable more flexible wallet functionality, but delegated permissions must be managed carefully.
In the reported attack, the mechanism allowed unauthorized transfers to continue even after Binance suspended withdrawals. The exchange said its multiparty computation, or MPC, wallet system also complicated efforts to revoke the permissions.
MPC distributes control over transaction signing rather than relying on one private key held in a single location. Although this approach is designed to strengthen wallet security, Binance’s account indicates that the interaction between the delegated permissions and its signing arrangements made the response more difficult. Technical details about EIP-7702 are available in the official Ethereum Improvement Proposal.
Binance Reports $2.85B Frozen or Intercepted
The breach affected approximately $6.3 billion in digital assets. Binance said $2.85 billion had been frozen or intercepted in its latest accounting. The exchange also stated that it would absorb the losses rather than pass them on to customers.
As of October 31, Binance said it had replenished 98% of the affected token assets. The figure describes the exchange’s reported recovery and replenishment efforts following the incident; it does not mean that all stolen funds were recovered.
The scale of the reported loss makes the incident a major security event for the cryptocurrency industry. The attack also raises questions about how exchanges protect employees with access to sensitive infrastructure, particularly against social engineering campaigns that use familiar workplace processes such as recruitment and software development.
FBI Attribution and North Korea’s Denial
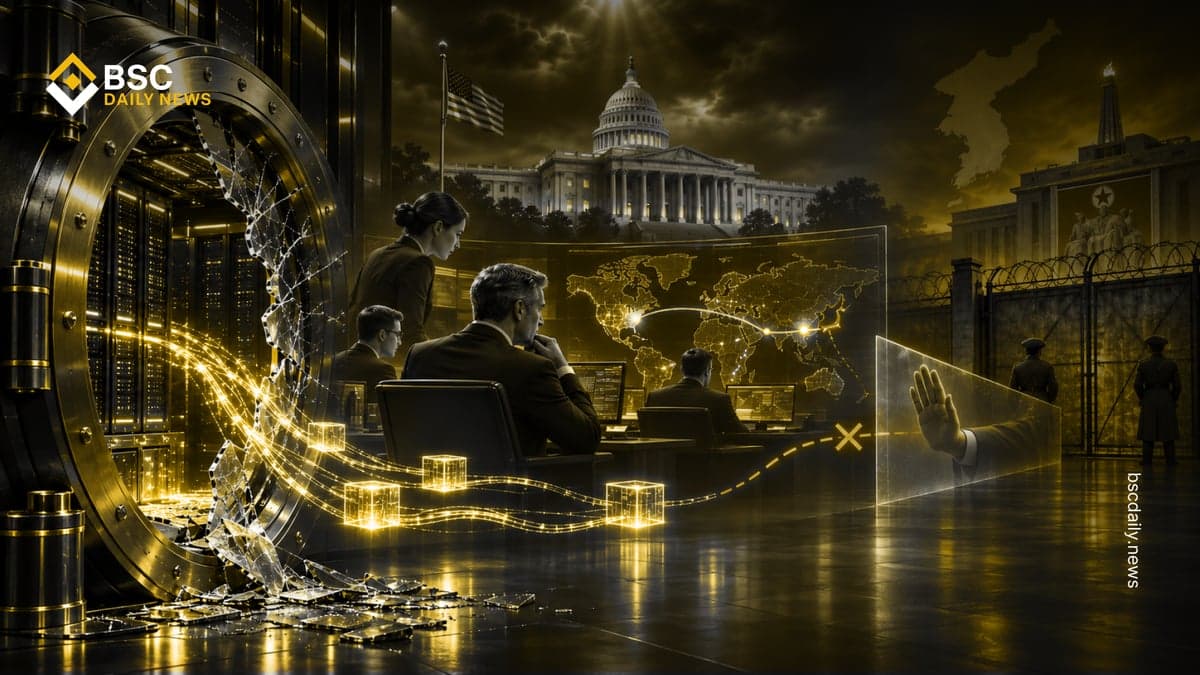
The Federal Bureau of Investigation has attributed the attack to North Korean hackers. North Korea has denied involvement. On Tuesday, Kim Yo Jong, the sister of North Korean leader Kim Jong Un, rejected the attribution and described the FBI’s claim as politically motivated and intended to damage the country’s international standing.
The competing positions leave the attribution disputed in the supplied information. The FBI’s assessment and North Korea’s denial should therefore be treated separately from the technical attack sequence described in Binance’s postmortem.
Binance Says It Blocked 57 Suspected Cyber Threats in 2026
Binance co-founder Yi He said the exchange’s security team had detected and prevented 57 suspected North Korea-linked cyber threats during 2026. She said the attempts included fraudulent job interviews, malicious software packages and social engineering tactics designed to steal credentials or install malware.
“We intercepted many of them, but the cost of failing to stop even one was severe—and this should never have happened,” Yi He said in a post on X.
Her comments point to the continued use of employee-focused attacks against cryptocurrency companies. Binance’s investigation suggests that the October 29 breach developed through several stages, beginning with compromised software and a fake recruitment exercise before reaching wallet-signing infrastructure.
The incident underscores the importance of securing employee devices, verifying software downloads and protecting credentials used to deploy or manage critical systems. For cryptocurrency exchanges, those safeguards are closely connected to the security of customer assets.